Enterprise-Level Protection.
Right-Sized Cybersecurity & Privacy Advisory for Every Stage of Growth
Every business faces the same data privacy regulations, breach risks, and compliance obligations as Fortune 500 firms — without their internal security teams, legal departments, or budgets. Sitoo Advisory closes that gap with certified, hands-on advisory right-sized to your organization.
enterprise environments
security certifications
try before you buy
jargon. No gimmicks.
The reality regulators won’t soften for you: GDPR, CCPA/CPRA, HIPAA, and state privacy laws apply to your business regardless of size — and a data breach or non-compliance finding hits a 30-person company far harder than a Fortune 500. Most vendors sell you tools. Sitoo Advisory builds the actual program.
Built for Every Stage — From Startup Through Enterprise.
From founders standing up their first security program to mid-market teams scaling into regulated industries to enterprise organizations maturing their privacy posture — Sitoo Advisory delivers the program, the certifications, and the accountability that close exposure at the scale your organization can act on today.
Regulation Doesn’t Scale Down by Headcount
If you handle customer data — in California, the EU, Mexico, Brazil, Colombia, Argentina, Chile, or any jurisdiction with active privacy laws — your business is subject to GDPR, CCPA/CPRA, HIPAA, LGPD, LFPDPPP, SOC 2, and local data-protection regimes. State attorneys general in the US, the AEPD in Spain, the ANPD in Brazil, and data protection authorities across Latin America are actively pursuing organizations of every size. “We’re too small to matter” is not a legal defense in any jurisdiction.
Vendors Sell Tools. Nobody Builds the Program.
Most organizations end up with a stack of disconnected security tools, a compliance checklist they don’t fully understand, and no one accountable for whether any of it actually reduces their risk. That’s not a security program — that’s managed exposure.
Proven & Certified Advisory.
Enterprise experience. Boutique execution.
Sitoo Advisory delivers IAPP- and ISACA-certified expertise directly to your organization. No junior consultants. No layered delivery teams. No account-manager bottlenecks — direct, senior-led accountability for strategy, execution, and outcomes.
- 10+ Yrs Experience
- IAPP Certified
- ISACA Certified
- Cybersecurity
- Privacy
- Data Protection
The Program Your Business
Actually Needs.
Every engagement is scoped to your regulatory obligations, data environment, and risk tolerance — not a template designed for a company ten times your size. Every service includes defined deliverables, not open-ended hours.
Data Protection & Privacy Operations
CIPP/US, CIPP/E, and CIPM-certified privacy program design — gap assessments, DPIAs, data mapping, RoPA, DSAR workflows, and cross-border transfer compliance built for your jurisdictions.
Learn MoreGRC & Regulatory Compliance Advisory
Framework-aligned compliance programs scoped to what your clients, partners, or regulators actually require. SOC 2, ISO 27001, NIST CSF — audit-ready evidence from day one.
Learn MoreRisk Assessment & Cyber Risk Quantification
Technical findings translated into business decisions. Risk register, NIST CSF 2.0 maturity scoring, control effectiveness testing, and executive briefings your leadership team can act on.
Learn MoreDLP Management
Turn sensitivity labels into enforcement — endpoint, email, and cloud DLP designed against your regulatory drivers. Microsoft Purview-led, monitor-mode tested, tuned to stop exfiltration without burying your team in noise.
Learn MoreIT Audit & Control Assurance
Independent ITGC reviews, access and change management audits, and organized evidence packages — Big 4 rigor at a fraction of the cost and timeline.
Learn MoreThird-Party Risk Management (TPRM)
Vendor relationships are your largest uncontrolled attack surface. Sitoo maps, tiers, and assesses every third party with access to your data and systems — and builds the program that keeps it current.
Learn MoreRemediation as a Service
Most advisors hand you a report and walk away. Sitoo stays through closure — roadmap, implementation support, policy drafting, tool configuration, retesting per contractual terms, and an auditor-ready closure report.
Learn More- Prioritized remediation roadmap with owners & deadlines
- Hands-on implementation support for controls & tooling
- Policy & procedure drafting aligned to your framework
- Retesting of every finding in accordance with the contractual terms and conditions
- Auditor-ready closure report for stakeholders
Covering GDPR · HIPAA · SOC 2 · ISO 27001 · PCI DSS · CCPA/CPRA · LGPD · NIST CSF · and more — See all 14 frameworks →
Not Sure What You Need? Start Here.
Pick the sentence that sounds most like your week. We’ll point you to the right service — no acronyms required.
Data Protection & Privacy Operations
We build the workflow that finds, exports, and deletes a person’s data on request — and the map of where it all lives — so these requests stop being fire drills.
See the serviceGRC & Regulatory Compliance Advisory
We scope the framework, close the control gaps, and get you audit-ready — without you hiring a full-time compliance lead to do it.
See the serviceGRC & Compliance + Privacy Operations
We run a HIPAA gap assessment against how you actually operate, then hand you a prioritized fix list — not a 90-page report you’ll never read.
See the serviceRisk Assessment & Cyber Risk Quantification
We score your exposure against NIST CSF 2.0 and CIS Controls and rank it, so your limited budget goes to the gap that would actually hurt you most.
See the serviceDLP Management
We configure Microsoft Purview to catch and block sensitive data before it leaves — across email, laptops, and cloud apps.
See the serviceIT Audit & Control Assurance
We run the access and systems reviews your auditors expect and hand back a clean evidence package — so audit season stops derailing your team.
See the serviceThird-Party Risk Management
We inventory your vendors, rank them by risk, and review the contract terms — so one weak supplier doesn’t become your breach headline.
See the service★ Remediation as a Service — our flagship
This is exactly the gap we built for. We close the findings, retest them, and prove it in writing. Remediation should close risk, not generate new billable hours.
See the engagement modelStill not sure? Book a 30-minute risk briefing and we’ll tell you where to start.
From Where Your Data Lives to How It’s Protected.
Five progressive stages — each engagement builds on the last. One program that connects every service Sitoo delivers.
What You Get That No
Vendor Will Offer You.
Holistic, Not Compartmentalized
Most vendors solve one layer — a tool, a checklist, or a single regulation. Sitoo Advisory assesses the full data lifecycle: where your sensitive data lives, how it moves, who touches it, and where your regulatory exposure actually sits. Then builds the program to address all of it.
Try Before You Buy — No Retainer Required
No six-figure commitment to get started. Sitoo Advisory’s engagement model lets you experience the depth and quality of the work before any long-term commitment. You see the value before you fund it. That’s the model — not a promotional offer.
Contractual Retesting — No Asterisks
Remediation should close risk, not generate new billable hours. Every assessment includes retesting of remediated controls in accordance with the contractual terms and conditions so you can confirm findings are genuinely resolved — and demonstrate that to auditors, clients, or regulators when they ask.
Fortune 500 Advisory.
Built for Every Business.
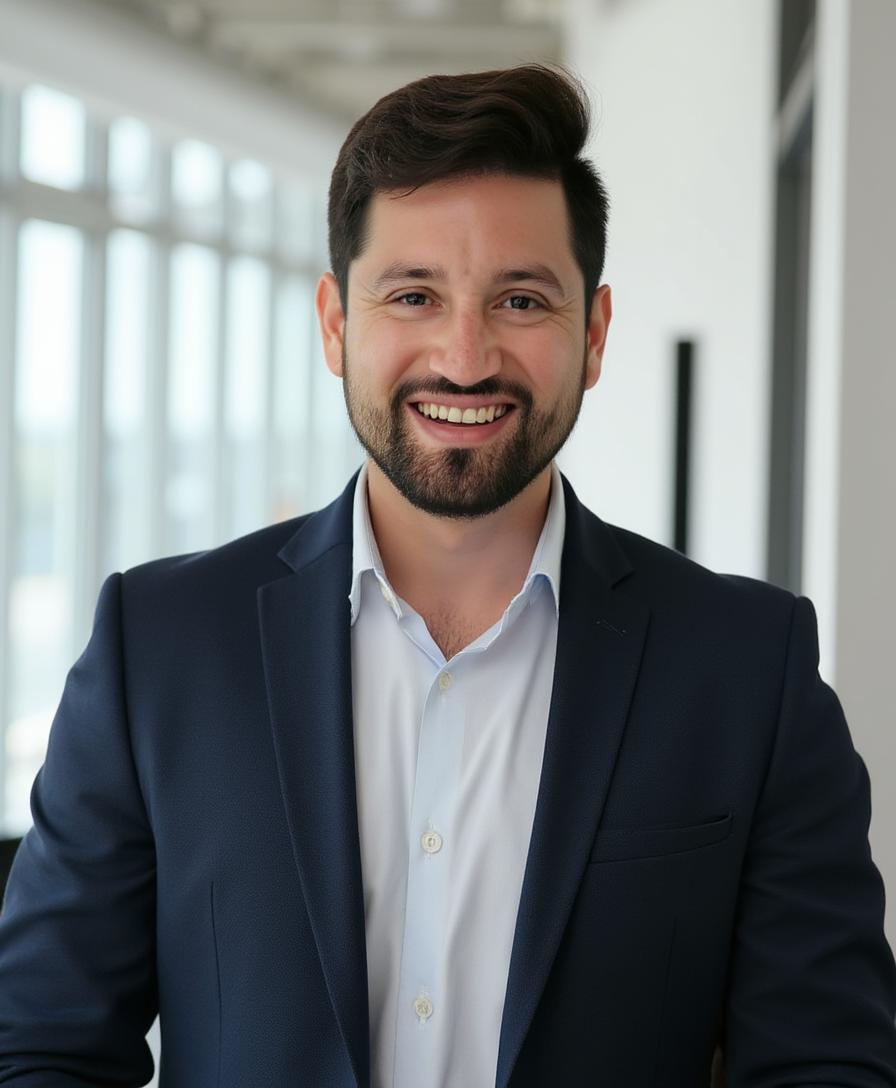
Juan Molina spent more than a decade inside Fortune 500 companies in regulated industries — where the gap between vendor promise and operational delivery becomes regulatory action, litigation, and reputational damage. That gap is exactly where Sitoo Advisory operates: hands-on expertise and direct, senior-led accountability — not just what shows up in a report.
Full bio, credentials & background →“Companies are not protected by their size — they are targeted precisely because of how attackers calculate effort versus reward. The same regulatory obligations, the same attacker interest, often with a fraction of the internal resources to respond. That asymmetry is exactly the problem Sitoo Advisory exists to solve.”
Find Out Exactly Where
Your Real Exposure Sits.
Schedule a no-commitment risk briefing. We identify the gaps your current program is missing — in plain language, tied to the regulations that apply to your business specifically.
What happens next: Within 1 business day, you’ll receive an acknowledgment and a proposed time. The briefing itself is 30 minutes, structured, and produces a one-page summary of the highest-priority gaps in your current posture.